Notizia
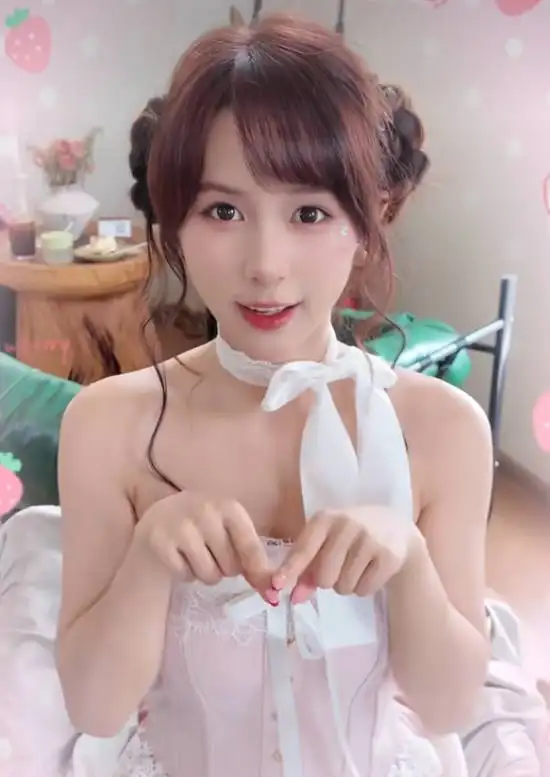
Bunny Garden 2 Adds Twin-Tail Lolita Roro in New Update
Bunny Garden 2's new 10-second trailer shows a twin-tailed lolita character in a sweet-yet-cutting promo. With six heroi




In May 2026, hacker group ShinyHunters claimed it had breached NVIDIA’s GeForce Now cloud gaming system. NVIDIA’s response drew a sharp line: the incident did not hit its self-operated global service, but the platform and database run by Armenian partner GFN.am.

The unsettling part is not just the word “breach.” It is how quickly the boundary of access can stop feeling clear. ShinyHunters said it obtained a complete user database containing names, email addresses, dates of birth, and membership status. That matters because the exposure was not partial or abstract; the claim was that core account information was sitting in one place, accessible once the side door gave way.
NVIDIA’s clarification is the key point here. According to the company, GeForce Now’s global first-party service was not compromised; the issue was confined to a regional partner inside the GeForce Now Alliance network. NVIDIA said the affected operator was GFN.am, whose service covers Armenia and extends into nearby countries including Azerbaijan and Georgia. The case lands on the weakest point of the alliance model: local partners can run independent databases to reduce latency, which improves service delivery, but it also fragments security oversight.

The bigger concern is that “no passwords leaked” does not mean “no real damage.” The exposed data reportedly also includes two-factor authentication metadata. That may sound less severe than a password dump, but it gives phishing attempts, credential-stuffing lures, and social engineering scams more precision. Once attackers know who you are, where you registered, and whether you are a member, those fragments can be assembled into a much more convincing profile.
From an industry perspective, NVIDIA has at least defined the line of responsibility clearly and said it is helping the partner investigate and fix the problem, with affected users to be notified directly. That is better than a vague statement, especially in cases where “third-party partner” can too easily become a catch-all shield. The practical problem is simpler: users do not separate self-operated infrastructure from alliance-hosted databases that neatly. Players only remember that they logged into GeForce Now.

If you are in a region covered by GFN.am and use the service, the immediate advice is straightforward: wait for the official notice, check the security of your email account right away, and be extremely cautious with unsolicited verification messages or “account recovery” links. Passwords were not exposed, but once the connected email address becomes a target, the follow-up fallout often starts there. For ordinary players, this is another reminder that cloud gaming is no longer competing only on bitrate, latency, and image quality. The distributed partner systems behind the scenes are becoming the next major test of trust.


Commenti 0
Ci interessa la tua opinione
Partecipa alla discussione e condividi la tua opinione su questo gioco.
Ancora nessun commento. Scrivi il primo.