News
Bunny Garden 2 Adds Twin-Tail Lolita Roro in New Update
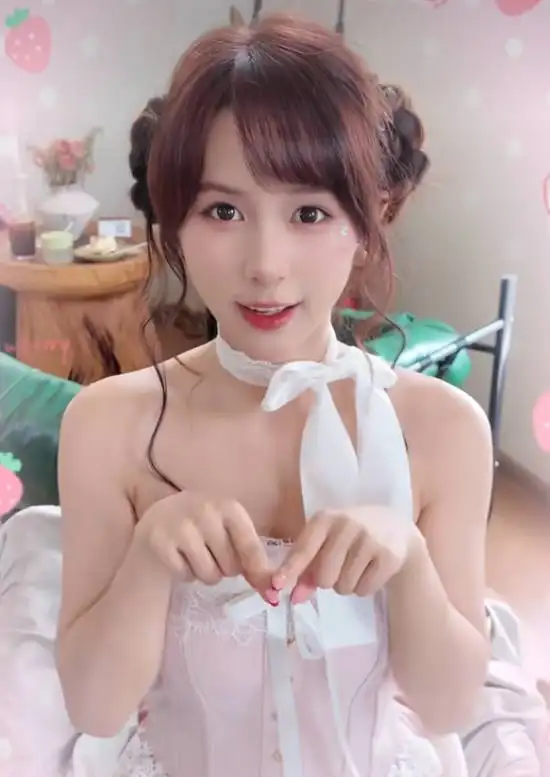
Bunny Garden 2's new 10-second trailer shows a twin-tailed lolita character in a sweet-yet-cutting promo. With six heroi

On May 4, Windows users worldwide faced a barrage of Microsoft Defender alerts flagging Trojan:Win32/Cerdigent.A!dha across legitimate software. Microsoft confirmed the incident as a mass false positive and issued an apology. The root cause traces back to a mid-April security breach at DigiCert, where hackers compromised a support analyst's device and stole private keys for approximately 60 customer code-signing certificates.

The fallout swept far beyond DigiCert's immediate customers. After the certificate authority revoked the compromised certificates, Defender flagged any program signed with them as malware—no questions asked. The detection logic went further off the rails when it started marking certificates unrelated to DigiCert, including Windows system root certificates. Fresh installs of Microsoft's own clean Windows ISOs triggered trojan warnings after updating the virus database, creating a circular problem where the operating system flagged itself as compromised.

Microsoft's statement acknowledged that "Defender's detection logic was overly aggressive" and promised adjustments to identify genuine malicious behavior rather than relying solely on certificate revocation as a threat indicator. This admission reveals a structural weakness: the current detection system leans too heavily on single-signal triggers without contextual analysis. If another certificate authority faces a similar breach, the same global false positive cascade could repeat.

Microsoft resolved the issue in security intelligence update version 1.449.430.0 and later releases. Windows 10, Windows 11, and Windows Server users can manually update their virus definitions to clear the false positives. The incident exposes a fragility in the digital certificate ecosystem—when a certificate authority's security fails, the trust chain collapses across every dependent system.

For users, the disruption hit hardest during routine tasks. Installing software or launching programs suddenly triggered trojan warnings, forcing a split-second judgment call: actual infection or system malfunction? The "better safe than sorry" approach reduces the risk of missing real threats, but repeated false alarms erode trust in security software. Microsoft needs tighter calibration between false positive rates and detection accuracy. If similar incidents recur without improvement, users may start disabling real-time protection entirely rather than dealing with constant interruptions.



Comments 0
Share your game review
Join the discussion and share your review of this game.
No comments yet. Share your review.