News
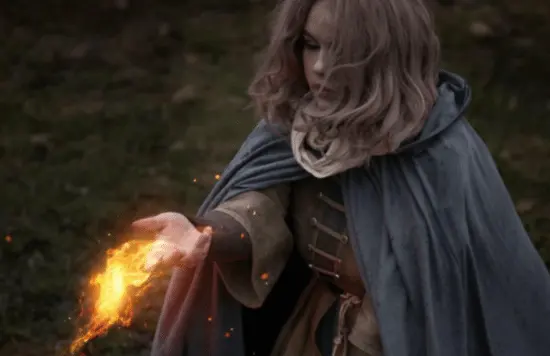
Elden Ring Cosplay Goes Full Post-Production, Is It Still Cosplay?
A Reddit user shared a Melina and Ranni cosplay from Elden Ring, with magic effects making it look close to the original

PlayStation Network is facing fresh scrutiny over account security after former IGN editor and Sacred Symbols host Colin Moriarty said on May 19, 2026 that his PSN account had been hacked. Hours later, he said he had recovered it through Sony’s official high-level channels. On the same day, creator @Genki_JPN said his own account had also been compromised earlier this year, with about $50 from his PSN wallet spent on Roblox currency. Taken together, the two cases have shifted attention to PSN’s security model and, especially, how account recovery is handled.

What these accounts expose is not just another isolated theft. They point to a deeper problem in the system’s most important tradeoff. On any mature platform, the real question is never just whether an account can be recovered, but who is allowed to change its core credentials, especially the email address and 2FA. Based on the claims now circulating, players are not mainly angry that Sony is willing to refund losses. They want to know how 2FA could be bypassed, or why customer support appears able to reset it so quickly. If that gap is real, then the rest of the security stack starts to look far less meaningful.
From a design standpoint, account recovery is exactly the kind of process that should be intentionally cumbersome. It is a low-frequency, high-risk pathway, and efficiency should come second to control. The criticism surfacing across overseas social media centers on that point: whether PSN recovery relies too heavily on the judgment of frontline support agents instead of a rigid, standardized, auditable verification procedure. If recent purchase history and similar details are visible in the backend, then hackers and legitimate owners may end up holding near-identical answers. That is weak verification design, and it makes social engineering far too viable.

Moriarty’s case is especially troubling on the technical side. He said he had not fallen for a phishing site and had properly safeguarded sensitive information, yet still received system text messages saying his account email had been changed and 2FA had been forcibly disabled. More importantly, he regained control within hours after speaking publicly, using Sony’s official higher-tier channels. Moriarty himself said that speed was tied to his industry profile and personal connections, and that ordinary players would not necessarily get the same treatment. If a system can only correct errors quickly for well-connected users, then the process is not really productized. It is being patched by manual exceptions.
The experience shared by @Genki_JPN pushes the issue beyond a single anecdote. He said, "My PSN account was also hacked earlier this year." After the account’s email was changed, about $50 from his wallet was used to buy Roblox currency. He later contacted official PlayStation support, recovered the account quickly, and received a full refund for the stolen funds. That suggests Sony’s current approach is closer to commercial damage control: reimburse first, calm users first, but offer too little public explanation of the exploit itself, the status of any fix, or why 2FA failed in the first place. That kind of communication leaves plenty of room for community backlash to keep growing.

From a business perspective, the real risk is not eating a single $50 refund. It is users starting to reassess the safety of their digital assets. A PSN account is not just a wallet. It also holds a game library, subscription benefits, save data, and payment relationships. Once players start to believe an account can be taken through customer-service social engineering, trust in the whole platform becomes more expensive to maintain. The situation looks worse because some users say the current process can hurt legitimate customers too. One person claimed that after contacting support to change a password because of a Sony system update bug, they were treated strictly and then remained locked out of their game library. That suggests a design that may be exploitable by attackers while also punishing normal users.
The practical advice for players is simple, but necessary. First, if 2FA is not enabled, turn it on as soon as possible. It remains the cheapest baseline defense. Second, keep records of device history and purchase receipts tied to the account. They may not be perfect proof, but they are better than trying to reconstruct everything from memory. Third, if the account is already protected by stronger verification methods, avoid changing those bindings unnecessarily. What Sony actually needs to fix is not its support script, but the chain that governs 2FA resets and email changes. That should be treated as a high-privilege backend process with long cooldowns, multiple review points, and several days of internal verification. Put plainly, account security is not an after-sales issue. It is platform infrastructure, and Sony has not publicly offered detailed explanations of the vulnerability, repair progress, or a formal response. If that does not change, more players are likely to get caught in the same system.



Comments 0
Share your game review
Join the discussion and share your review of this game.
No comments yet. Share your review.